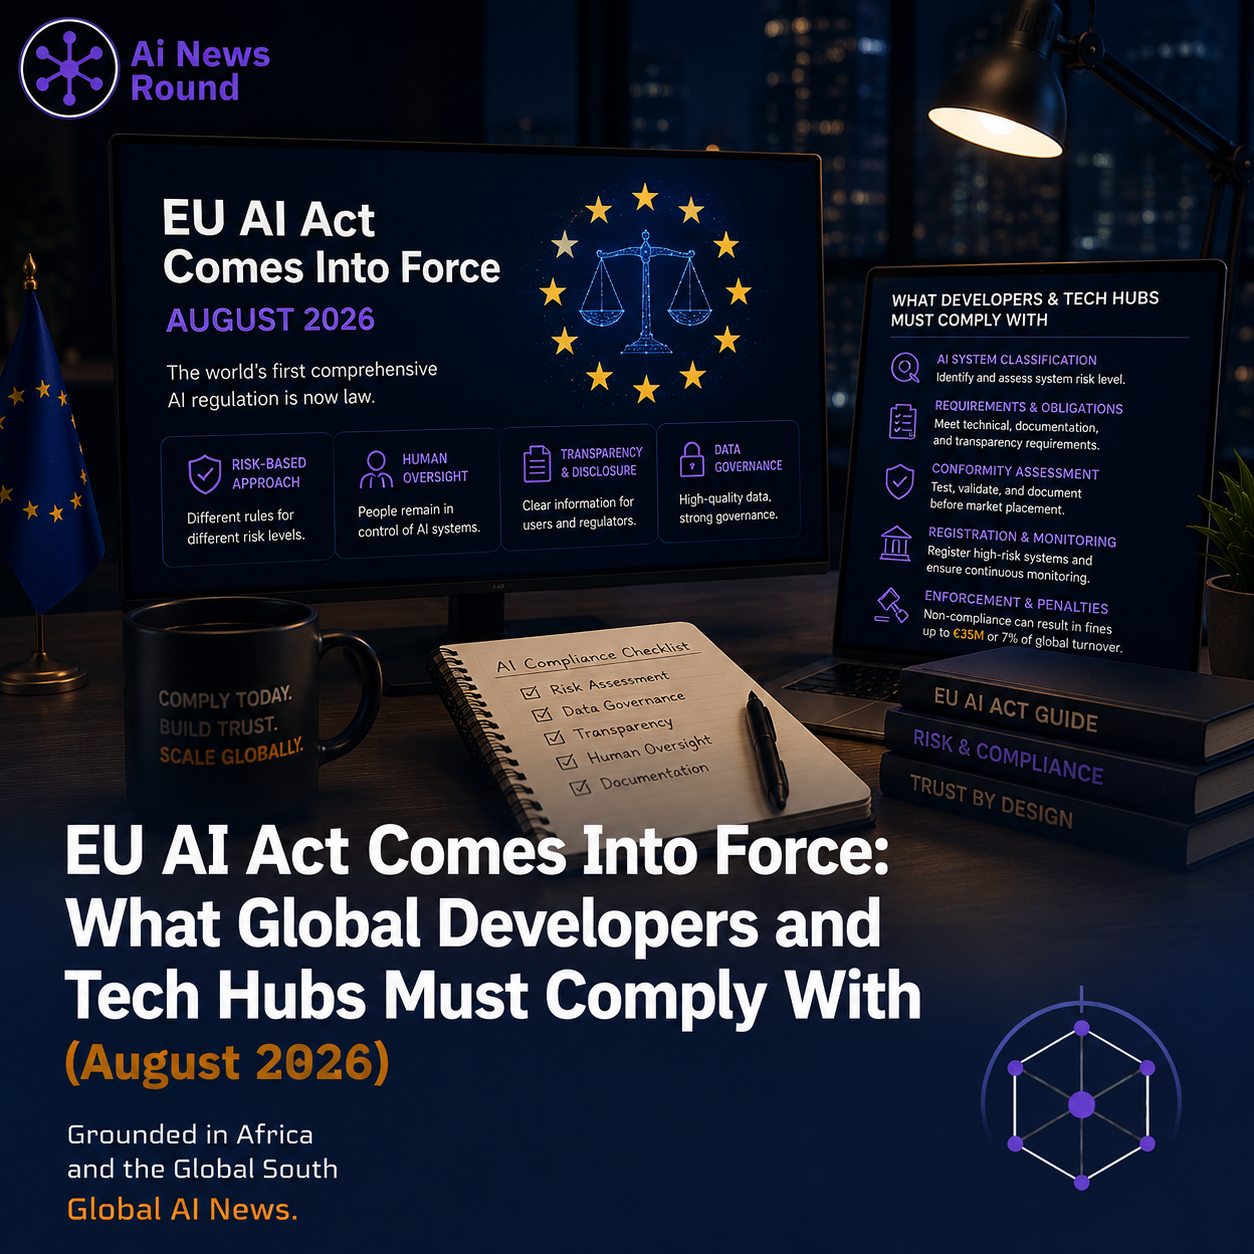
August 2026 marks a historic turning point in digital governance: the full enforcement of the European Union AI Act's transparency and General-Purpose AI (GPAI) provisions.
The regulatory framework transitioned from policy draft to active enforcement under the EU AI Office. If your engineering team deploys models globally or serves users in the European market, your technical stack is now subject to these legal boundaries.
The Core Mandates Active Now
While full high-risk system rules phase in over the coming years, the mandates that took effect on August 2, 2026, directly target foundation model providers and deployers:
GPAI Transparency Obligations: Providers of general-purpose models must publish detailed technical documentation, training data summaries, and copyright policy compliance proofs.
AI-Generated Content Marking: Watermarking and machine-readable metadata standards are now mandatory for synthetic media, text, and audio generated within or exported to EU jurisdictions.
Cybersecurity & Evaluation Benchmarks: The EU Action Plan on Cybersecurity and AI establishes standardized third-party evaluation capacity for frontier risk, biosecurity, and systemic resilience.
Review official compliance guidelines and text via the European Commission AI Office.
Why This Matters for Global and Emerging Market Developers
Regulations enacted in Brussels rarely stay in Brussels. The global reach of API-driven software means engineering teams in North America, Asia, and across Africa must align their data logging, user data flows, and output watermarking with EU baseline standards to serve international clients without friction.
Open-source maintainers must also take note: while pure research models enjoy targeted exemptions, any model deployed commercially or integrated into production API pipelines falls squarely under the new transparency framework.
What It Means for You
For CTOs and software architects, compliance is now an architectural requirement rather than a post-launch legal review. Auditing model provenance, output watermarking pipelines, and user data routing must be built into your CI/CD pipelines.